French supermarkets hit by cyberattack that forced fridges to defrost
Hundreds of French supermarkets suffered millions in food losses after hackers exploited outdated Danfoss controller firmware to turn refrigeration units into ovens.

- Core Development: Hundreds of French supermarkets suffered millions in food losses after hackers exploited outdated Danfoss controller firmware to turn refrigeration units into ovens.
- Beat Context: Categorized under Business with independent corroboration.
- Reporting Depth: 5 minute analytical read synthesized from verified newsroom sources.
On the morning of 13 October, a coordinated cyber intrusion swept through hundreds of French supermarkets, turning refrigeration units into ovens and forcing retailers to dump millions of euros worth of food. The attack, which began late on 11 October, was traced to software vulnerabilities in Danfoss controllers that were still running obsolete firmware. As temperatures in affected fridges climbed to 50 °C, many stores had to discard fresh and frozen goods, and a few fires broke out inside the premises.
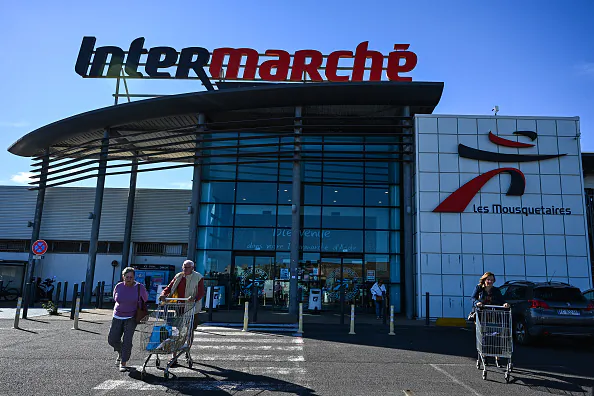
The first reports came from Intermarché, Cooperative U and E Leclerc. They confirmed that the attack had been carried out through remote management interfaces that had long been exposed to the internet. In the hours after the intrusion, workers found that the refrigeration systems were locked in a continuous defrost cycle, a setting that is normally used only for short periods to melt frost. The result was an explosive rise in temperature that turned the cold aisles into ovens, destroying produce and triggering combustion in some cases.
Media additions


According to the Cnet coverage, the hackers targeted the AK‑SM800 and AK‑SC355 models from Danfoss, which had not received security updates for months. Danfoss said it was working with affected customers to push firmware upgrades and to isolate the controllers from the public internet. The company noted that it had long advised supermarkets to move away from legacy equipment that no longer received patches.
French authorities reacted swiftly. The Al Jazeera report notes that the Paris prosecutor’s office opened a formal investigation and that Prime Minister Sebastien Lecornu ordered the National Cybersecurity Agency (ANSSI) to lead the probe. ANSSI has identified the Danfoss vulnerability and has reached out to European counterparts, as the attack may have reached stores in Spain, Portugal, Poland, Germany and Belgium, according to a source close to the investigation.
Intermarché’s chief executive, Thierry Cotillard, said the losses across the country could reach tens of millions of euros in a single day. The French retail federation (FCD) has called on Danfoss to provide full transparency, arguing that the legacy equipment was the weak link that allowed the breach to spread so widely.
In the weeks that followed, several retailers reported specific damage figures. Cooperative U’s network lost more than 100 outlets, while Monoprix reported that about 5 % of its 490 stores were affected. Carrefour said 80 supermarkets were impacted, and E Leclerc confirmed that a number of its stores fell victim to the cyber‑attack.
| Chain | Number of Stores Affected | Reported Losses (Approx.) |
|---|---|---|
| Intermarché / Netto | ≈300 | — |
| Cooperative U (Super U) | ≈100 | — |
| Carrefour | ≈80 | , |
| Monoprix | ≈25 (5 % of 490) | , |
| E Leclerc | , | , |
The incident has sent shockwaves through the food supply chain. In a statement, the French Ministry of Agriculture emphasised that the attack highlighted the need for greater security in the cold‑chain sector. EU food and agriculture commissioner Christophe Hansen condemned the event on social media, calling the “exploitation of food” a new reality that demands urgent attention.
Beyond the immediate losses, the attack raised questions about insurance coverage for cyber‑induced physical damage. Traditional cyber policies typically cover data recovery and business interruption, but the destruction of physical goods and fire damage may fall under property or fire insurance. Several retailers have expressed uncertainty over whether their policies will cover the spoilage and the cost of replacing damaged refrigeration units.
Experts argue that the attack illustrates the growing threat to operational technology (OT) across critical infrastructure. Nathaniel Jones, a senior vice president at a leading cyber‑intelligence firm, warned that OT systems, especially those that are internet‑connected, can be manipulated to cause real‑world harm. The incident also echoes earlier attacks on U.S. Military commissaries and highlights the vulnerability of essential services to remote manipulation.
In terms of technical root causes, Danfoss controllers used legacy protocols such as BACnet and Modbus, which lack built‑in authentication. Once the controllers were compromised, the attackers sent commands to keep the defrost heaters running continuously, effectively turning the refrigeration units into ovens.
French authorities are also looking into whether the breach was part of a broader state‑sponsored effort. The attack’s scale, the choice of a critical infrastructure target, and the absence of a ransom or data theft suggest a motive beyond conventional cybercrime. Analysts note that the incident aligns with recent Russian hybrid warfare tactics aimed at destabilising European supply chains.
For retailers, the immediate focus is on restoring normal operations. Danfoss has urged its customers to apply the latest firmware and to isolate their controllers from the public internet. Many supermarkets are also conducting internal reviews of their network segmentation, ensuring that OT and IT networks remain separate, and are installing industrial intrusion detection systems to monitor for abnormal behaviour.
On the policy front, the French government has announced a review of national cyber‑security standards for food retailers. The review will consider mandatory firmware updates for legacy equipment and will explore the possibility of new regulations that require retailers to demonstrate that their refrigeration systems meet minimum security benchmarks.
Looking ahead, the attack serves as a wake‑up call for the entire retail sector. As more stores adopt remote monitoring and maintenance, the risk of similar breaches increases. The incident also underscores the need for clear insurance frameworks that cover both data and physical damage, as well as the importance of rapid incident response that can mitigate loss before it escalates.
In the days following the attack, ANSSI will continue to investigate the origin of the breach, while retailers will work to replace damaged stock and repair damaged equipment. The European Union is expected to issue guidance on securing critical infrastructure, and insurers may revise policy language to address the new class of cyber‑induced physical loss. The full financial impact will become clearer as loss assessments are completed, but the scale of the damage is already evident in the tens of millions of euros lost across the country.
How significant is this development?
Contribute your assessment to the aggregated reader sentiment ledger.
Frequently Asked Questions
Key questions answered in this reportWhat is the key development in: French supermarkets hit by cyberattack that forced fridges to defrost?
Hundreds of French supermarkets suffered millions in food losses after hackers exploited outdated Danfoss controller firmware to turn refrigeration units into ovens.
Why is this Business development significant for the UK?
This report covers critical events in our Business beat. Independent reporting monitors related UK statements, regulatory shifts, and public responses as further verified details emerge.
How was this reporting corroborated and verified?
Newsarchy UK compiles and cross-references reporting from primary reporting from The Journal and cross-checked wire reports. All coverage adheres to published editorial standards.
When was this report published?
This briefing was published on October 13, 2026 and is permanently cataloged in the Newsarchy UK Business archives.